
Security assurance has become table stakes in the European crypto space as MiCA took full effect on 1 July 2026, while banks, asset managers, and PSPs from the TradFi spaces are beginning to serve as Crypto-assets Service Providers (CASPs) to support stablecoin and other digital currency transfers.
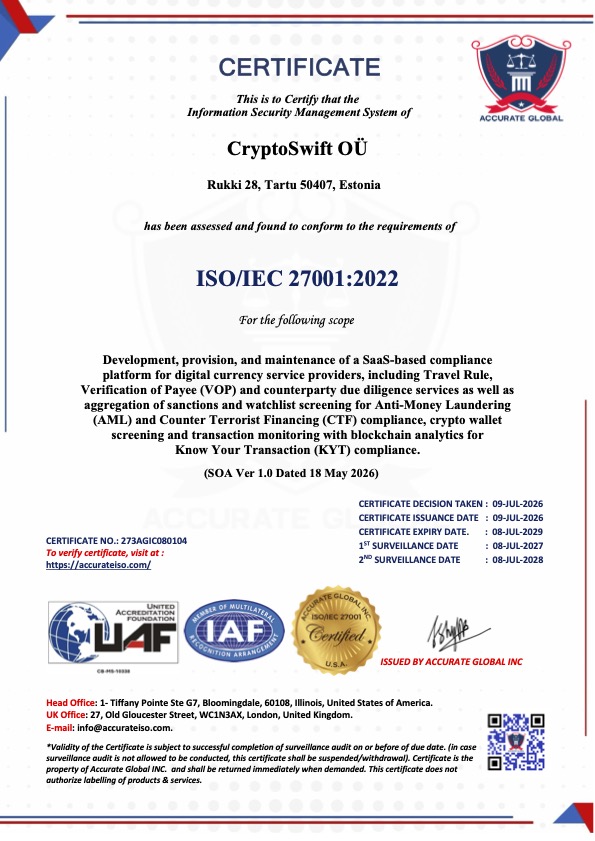
Beyond protecting our clients and their users, the convergence of crypto and traditional finance spurred CryptoSwift to obtain its ISO 27001 certification. This qualification demonstrates alignment with requirements placed on our European clients under the Digital Operational Resilience Act (DORA)
Given that CryptoSwift is the only EU-native Travel Rule provider on the market, and as such a unique Critical or Important Function (CIF) vendor in the EU’s financial industry supply chain, it become all the more important to signal that CryptoSwift follows the best practices in software and data security.
Our ISO certificate #273AGIC080104 can be verified at https://accurateiso.com.